AMM Vulnerabilities and Exploits: A DeFi Security Guide
 Nov, 8 2026
You put your money in a liquidity pool because it seemed safe. The code was audited. The protocol had billions in TVL. Then, overnight, the price crashed to zero, or worse, you found out someone drained the entire pool using a trick you didn't know existed. This isn't just bad luck; it's the reality of Automated Market Makers (AMMs) in decentralized finance.
If you're trading on platforms like Uniswap or Curve, you aren't just betting on market direction. You're interacting with complex smart contracts that have specific weaknesses. Understanding these AMM vulnerabilities is the difference between keeping your capital and watching it evaporate. Let's break down exactly how these systems get hacked, why they fail, and what you can actually do about it.
What Exactly Is an AMM?
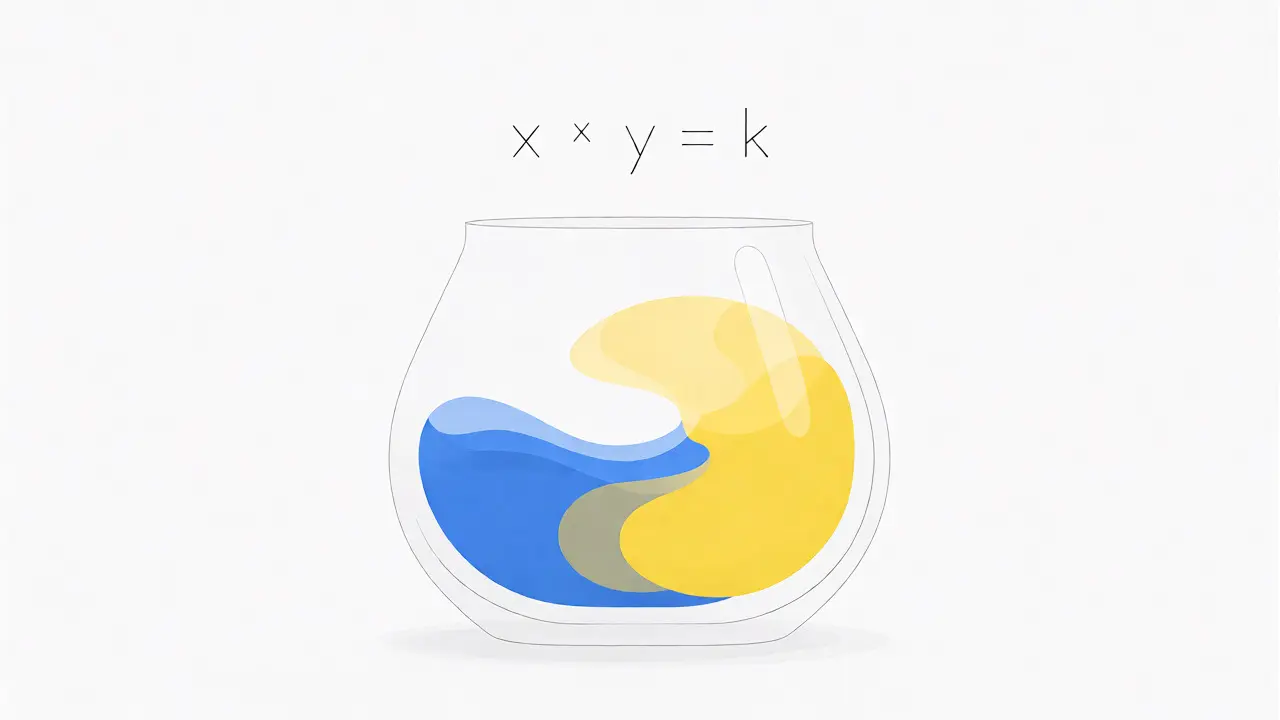
Before we talk about what breaks, we need to be clear on what we're dealing with. An Automated Market Maker is a type of decentralized exchange protocol that relies on a mathematical formula to price assets instead of an order book. Unlike traditional exchanges where buyers and sellers match orders, AMMs use liquidity pools.
Think of a liquidity pool as a giant pot containing two tokens, say ETH and USDC. Traders swap against this pot. The price changes based on the ratio of tokens in the pot. If someone buys a lot of ETH, there's less ETH in the pot, so the price goes up. It’s simple math, but the implementation is where things get tricky.
The most common formula is the constant product formula: $x \times y = k$. Here, $x$ and $y$ are the quantities of the two tokens, and $k$ is a constant. When you trade, $x$ and $y$ change, but $k$ stays the same. This mechanism creates liquidity without needing market makers to manually place bids and asks. But this simplicity hides several layers of risk.
The Flash Loan Attack: The Most Common Killer
If you only learn one exploit type, make it this one. A Flash Loan is an uncollateralized loan that must be borrowed and repaid within the same transaction block. It sounds impossible-how can you borrow millions without collateral? Because if you don't pay it back by the end of the transaction, the whole thing reverts, as if it never happened.
Attackers love flash loans because they give them massive buying power for free. Here’s how they exploit AMMs:
- The Setup: The attacker borrows a huge amount of Token A from a lending protocol like Aave.
- The Manipulation: They dump this borrowed Token A into a small liquidity pool on an AMM. This floods the pool, crashing the price of Token A relative to Token B.
- The Arbitrage: While the price is artificially low, they buy up all the cheap Token B from other pools or mint new LP tokens at a discount.
- The Reversal: They sell their acquired Token B back into the manipulated pool, restoring the price.
- The Profit: They repay the flash loan. The profit remains in their wallet.
This isn't just theoretical. In 2021, the Mango Markets exploit saw traders manipulate oracle prices using flash loans to drain over $100 million. The vulnerability wasn't in the loan itself, but in how the AMM or the lending protocol trusted a single spot price source that could be easily moved by large trades.
Sandwich Attacks: The Tax on Your Trades
You might not lose all your money in a sandwich attack, but you definitely lose value. This happens when bots monitor the public mempool-the waiting area for pending transactions. These bots see your trade before it gets confirmed on-chain.
Here’s the sequence:
- Front-Running: The bot sees you want to buy 10 ETH. It quickly submits its own buy order with higher gas fees, pushing the price up before yours executes.
- Your Trade: Your transaction goes through, but now you’re paying a higher price than you expected because the bot already bought some supply.
- Back-Running: Immediately after your trade confirms, the bot sells the ETH it bought earlier. Your purchase helped push the price up, so they sell high.
The result? You suffer from increased slippage. You paid more for the asset than the market average would suggest. For retail traders, this feels like hidden fees. For large whales, it can cost thousands of dollars per trade. This is a form of Maximal Extractable Value (MEV), which refers to the maximum value that can be extracted from blockchain transactions beyond the block reward and gas fees.
Oracle Manipulation: Garbage In, Garbage Out
Many AMMs don't operate in isolation. They rely on Oracles, services that feed real-world data onto the blockchain to determine prices, especially for assets that aren't directly traded in the pool or for lending protocols that use AMM prices as collateral values.
A classic mistake is trusting a single spot price from one exchange. If an attacker manipulates the price on that specific exchange using a flash loan (as described above), the Oracle reports the wrong price to the smart contract. The smart contract believes the asset is worth $100 when it's really worth $10. Lenders then issue loans against inflated collateral, leading to insolvency when the price corrects itself.
Protocols like Chainlink mitigate this by aggregating data from multiple sources and using time-weighted averages. But older or smaller AMMs often skip these safeguards to save on gas costs, leaving themselves wide open.
Smart Contract Bugs: The Code Is Law, Until It Isn't
Even with perfect economic incentives, code can fail. Smart contracts are immutable once deployed. If there's a bug, you can't just patch it like a website update. You need a migration plan, which takes time. During that time, hackers are busy.
Common coding errors include:
- Reentrancy Attacks: An external contract calls back into the original contract before the first execution is finished. This allows attackers to withdraw funds repeatedly before the balance is updated.
- Integer Overflow/Underflow: In older Solidity versions, numbers could wrap around. Subtracting 1 from 0 resulted in the largest possible number, allowing attackers to mint infinite tokens.
- Access Control Failures: Functions meant only for admins were left open to anyone. Sometimes, a "pause" function could be triggered by any user, freezing the entire protocol.
The Wormhole bridge hack in 2022, while not strictly an AMM, highlighted how critical signature verification bugs are. Similar logic errors in AMM fee distribution mechanisms have led to fund leaks where users could claim rewards multiple times.
Impermanent Loss: The Silent Erosion
This isn't a hack, but it is a vulnerability of the AMM model itself. When you provide liquidity, you earn fees. But if the price of one token moves significantly compared to the other, you might have been better off just holding the tokens in your wallet.
Why does this happen? Because the AMM automatically sells the rising asset and buys the falling one. You end up with more of the underperforming token and less of the outperforming one. If the price diverges too much, the losses from this rebalancing can outweigh the trading fees you earned.
For example, if you provide ETH/USDC liquidity and ETH doubles in price, you'll end up with half the ETH you started with. If you had just held, you'd have twice the value. With the AMM, you capture only part of that growth. This structural disadvantage is why many LPs prefer stablecoin pairs, where impermanent loss is minimal.
Comparing Major AMM Models and Their Risks
Not all AMMs are created equal. Different designs prioritize different features, which introduces different vulnerabilities. Here’s a quick look at the big players.
| Protocol | Type | Key Feature | Primary Vulnerability |
|---|---|---|---|
| Uniswap V3 | Concentrated Liquidity | Liquidity providers choose price ranges. | Complexity leads to poor range selection; MEV bots target active ranges. |
| Curve Finance | StableSwap | Optimized for similar-priced assets (stablecoins). | Vulnerable to de-pegs; if one coin loses peg, pool drains rapidly. |
| Balancer | Weighted Pools | Customizable token weights (e.g., 80% BTC, 20% ETH). | Rebalancing issues; sensitive to extreme volatility in weighted assets. |
| SushiSwap | Multi-Chain AMM | Forks of Uniswap with extra features. | Inconsistent audits across different chain deployments. |
Notice how Curve is great for stability but terrible if one of your stablecoins suddenly drops to $0.95. Uniswap V3 offers higher efficiency but demands more skill from LPs. Choosing the wrong platform for your risk tolerance is a vulnerability in itself.
How to Protect Yourself
You can't eliminate all risk, but you can reduce it significantly. Here’s a practical checklist for anyone interacting with AMMs.
- Check the Audit: Has the smart contract been audited by reputable firms like CertiK, Trail of Bits, or OpenZeppelin? Look for recent dates. An audit from 2020 doesn't protect you in 2026.
- Use Slippage Protection: Always set a reasonable slippage tolerance. Don't leave it at default. If you're doing a large trade, consider splitting it into smaller chunks to avoid moving the price yourself.
- Avoid Low-Liquidity Pools: Thin markets are easy to manipulate. Stick to pools with significant Total Value Locked (TVL) unless you know exactly what you're doing.
- Monitor Oracles: If you're using a lending protocol that relies on AMM prices, check which oracle they use. Chainlink is generally safer than proprietary spot-price feeds.
- Stay Updated: Follow security news. If a major bridge or aggregator has a breach, pause your activity until the dust settles.
Remember, decentralization means no customer support hotline. If you send funds to a buggy contract, they're gone. If an attacker drains the pool, there's no insurance company coming to bail you out. Your due diligence is your only safety net.
What is the biggest risk in using AMMs?
The biggest risks are smart contract bugs and economic exploits like flash loan attacks. Unlike centralized exchanges, if the code fails or an attacker manipulates the price, there is often no recourse to recover lost funds.
Can I prevent sandwich attacks?
You can minimize them by using private transaction relays (like Flashbots) that hide your trade from the public mempool until it is mined. You can also lower your slippage tolerance to make your trade less attractive to bots.
Is impermanent loss guaranteed?
No, it is not guaranteed. Impermanent loss occurs only if the price ratio of the paired tokens changes significantly during your investment period. If prices return to their original ratio, there is no impermanent loss.
Are audited protocols completely safe?
No. Audits reduce the likelihood of known bugs but cannot guarantee 100% security. New types of economic attacks or integration risks may emerge after the audit. Always assess the total value locked and community trust alongside audit reports.
What happens if an AMM oracle fails?
If an oracle provides incorrect price data, the AMM may trade at incorrect rates. This can lead to arbitrage opportunities for bots or liquidation cascades in lending protocols that rely on those prices for collateral valuation.